Fortinet Unified SASE, Deployed and Managed by eComms

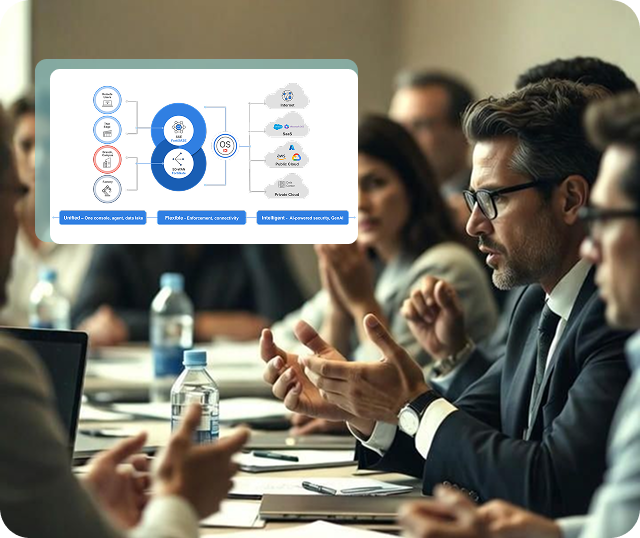
Converge your network and your security into one cloud-delivered platform. Fortinet single-vendor SASE gives every user the same protection whether they are in the office, at home, or on the road, and eComms configures and runs it for you. 

Talk to a SASE Specialist

    The Security Gap Hybrid Work Created

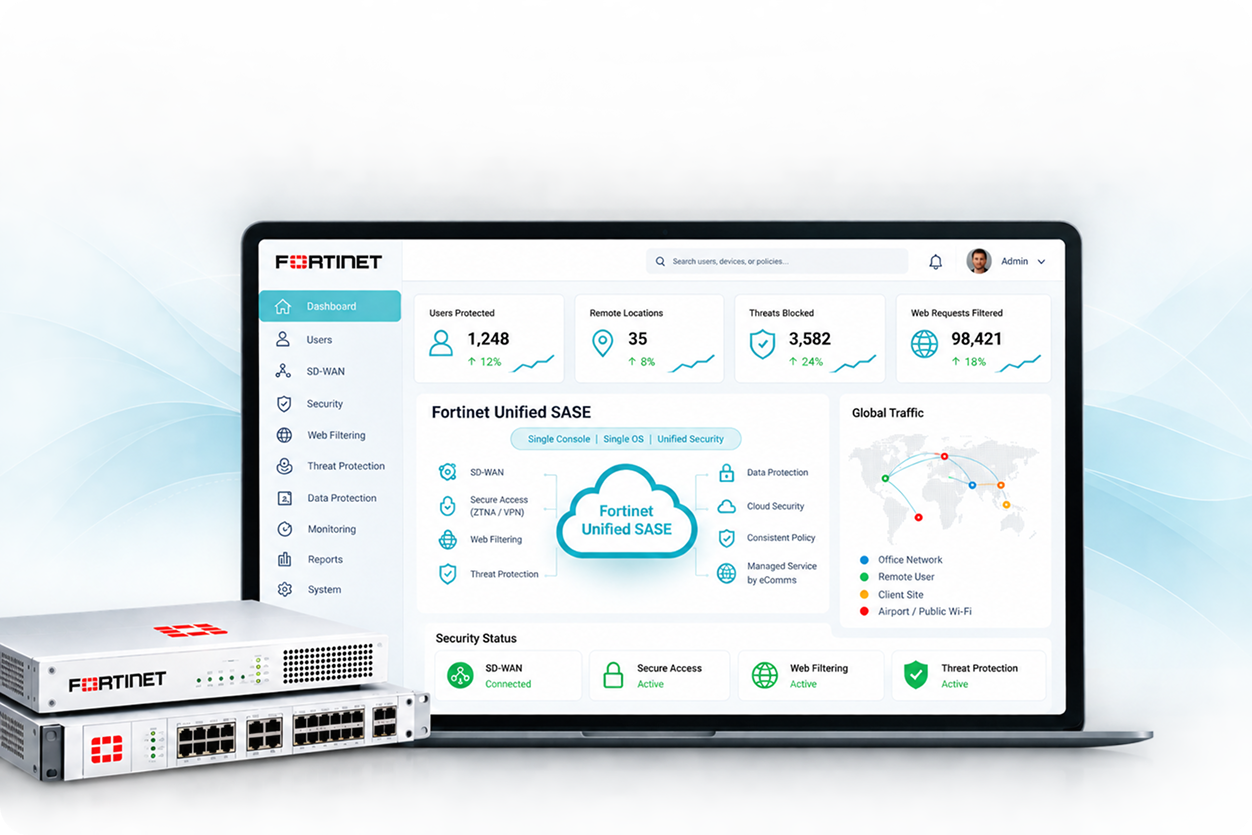
    Hybrid and remote teams are not on the corporate network when they work from home, a client site, or an airport lounge. A VPN gives them access, but it does not apply the same security policy as the office firewall. A separate web filtering tool protects internet-bound traffic, but it is a different console managed by a different team on a different update cycle. Fortinet Unified SASE closes this gap: SD-WAN and cloud security converged into a single platform, running on one operating system, managed from one console, so every user has the same protection regardless of where they connect from. eComms delivers Fortinet SASE as a managed service, not a product we sell and hand over. 

    What Fortinet Unified SASE Converges Into One Platform

    Five separate tools replaced by one integrated platform: 

    FortiSASE connects to existing SD-WAN or FortiGate firewall deployments at no additional licence cost. For eComms customers already running Fortinet infrastructure, extending protection to remote users is an operational decision rather than a new procurement. 
    Secure SD-WAN 

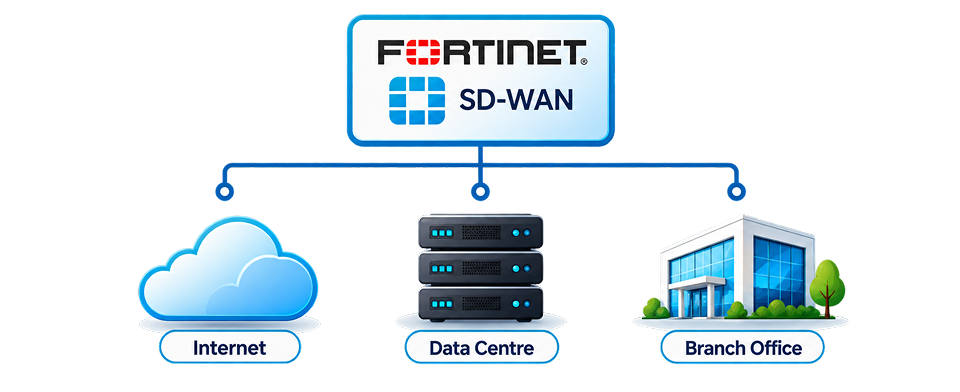
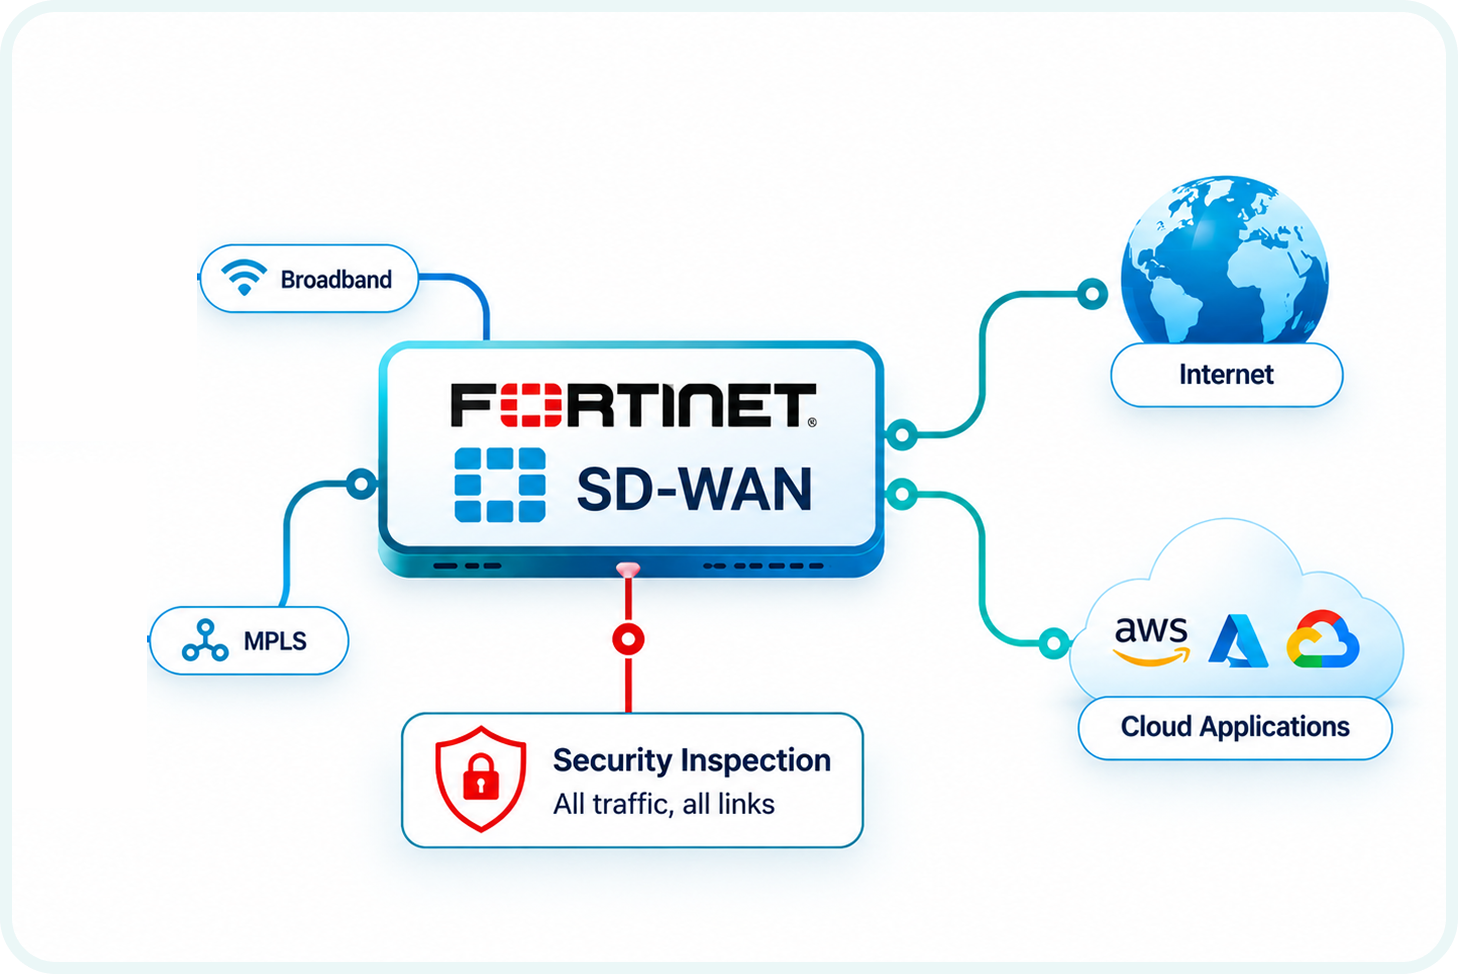
    Intelligent WAN routing across sites and cloud connections, with security inspection applied to all traffic regardless of which link it uses. See Fortinet SD-WAN for the full product detail.
    Secure Web Gateway 

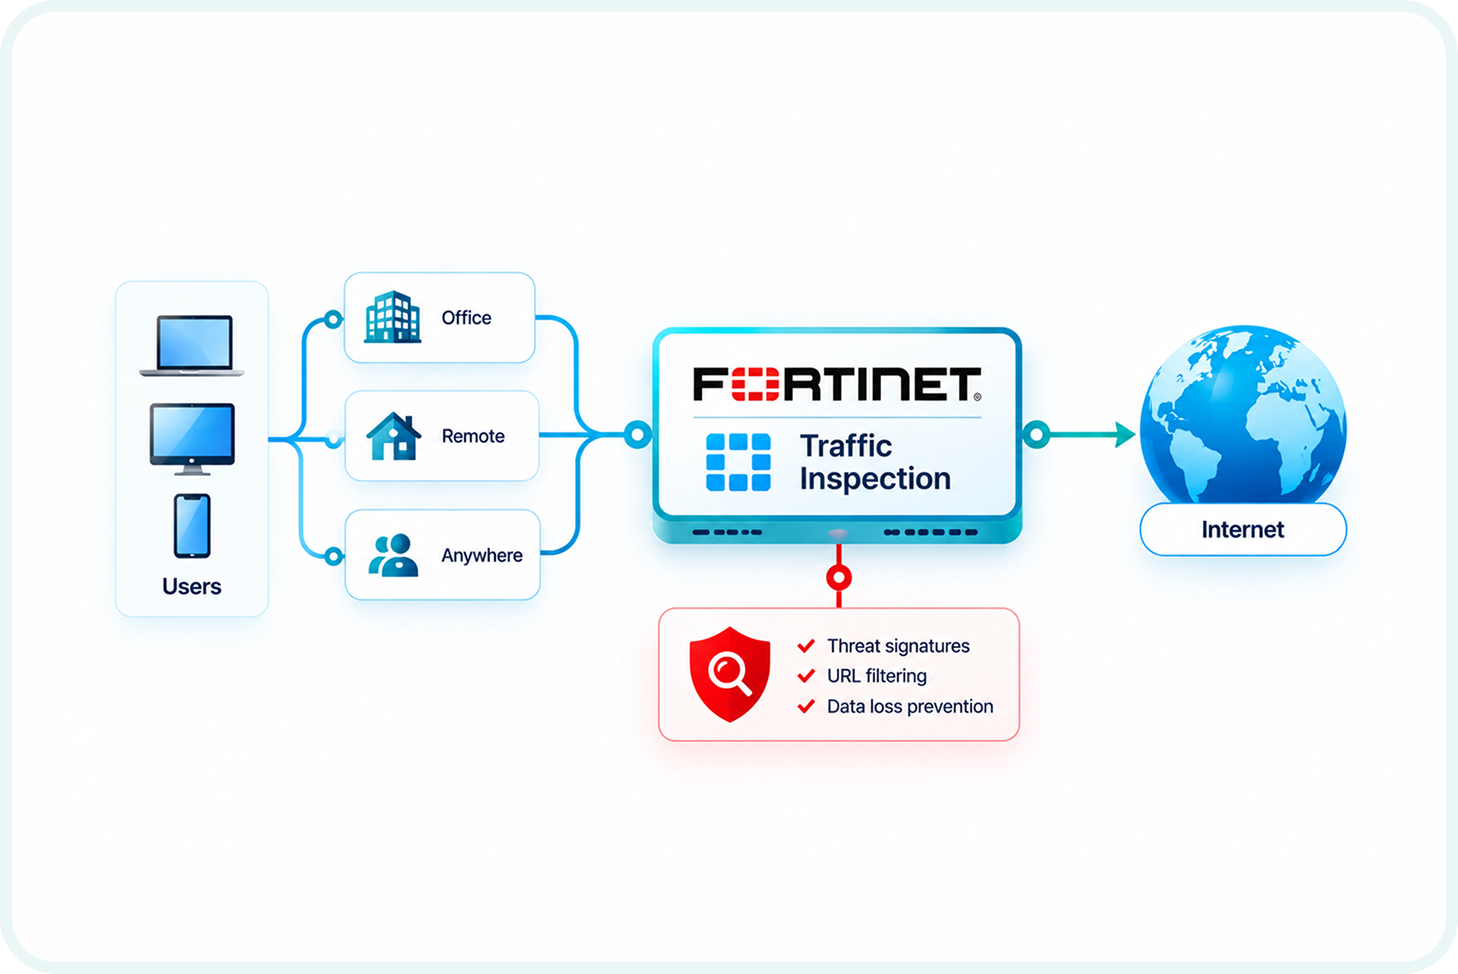
    All internet-bound traffic, from any user at any location, is filtered and inspected before it reaches its destination. Threat signatures, URL categories and data loss prevention policies apply uniformly. 
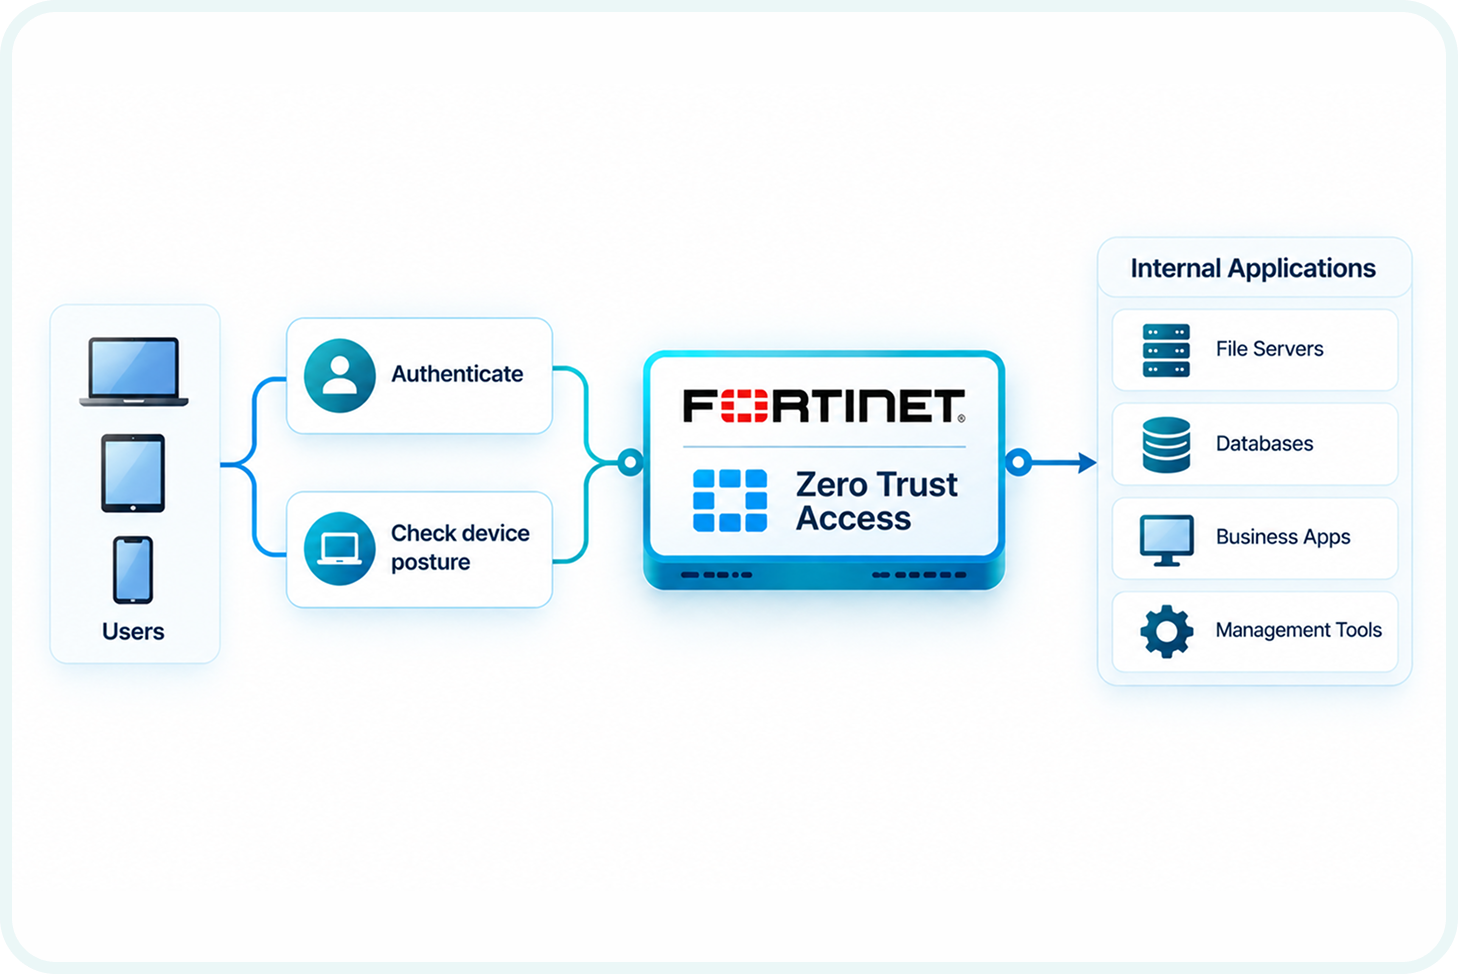
    Universal ZTNA 

    Zero trust access to internal applications. Users authenticate and device posture is checked before they reach any internal resource, replacing broad VPN tunnels with precise per-application access. Available at no additional licence cost on existing FortiGate or SD-WAN deployments. A significant cost point for businesses already running Fortinet. 
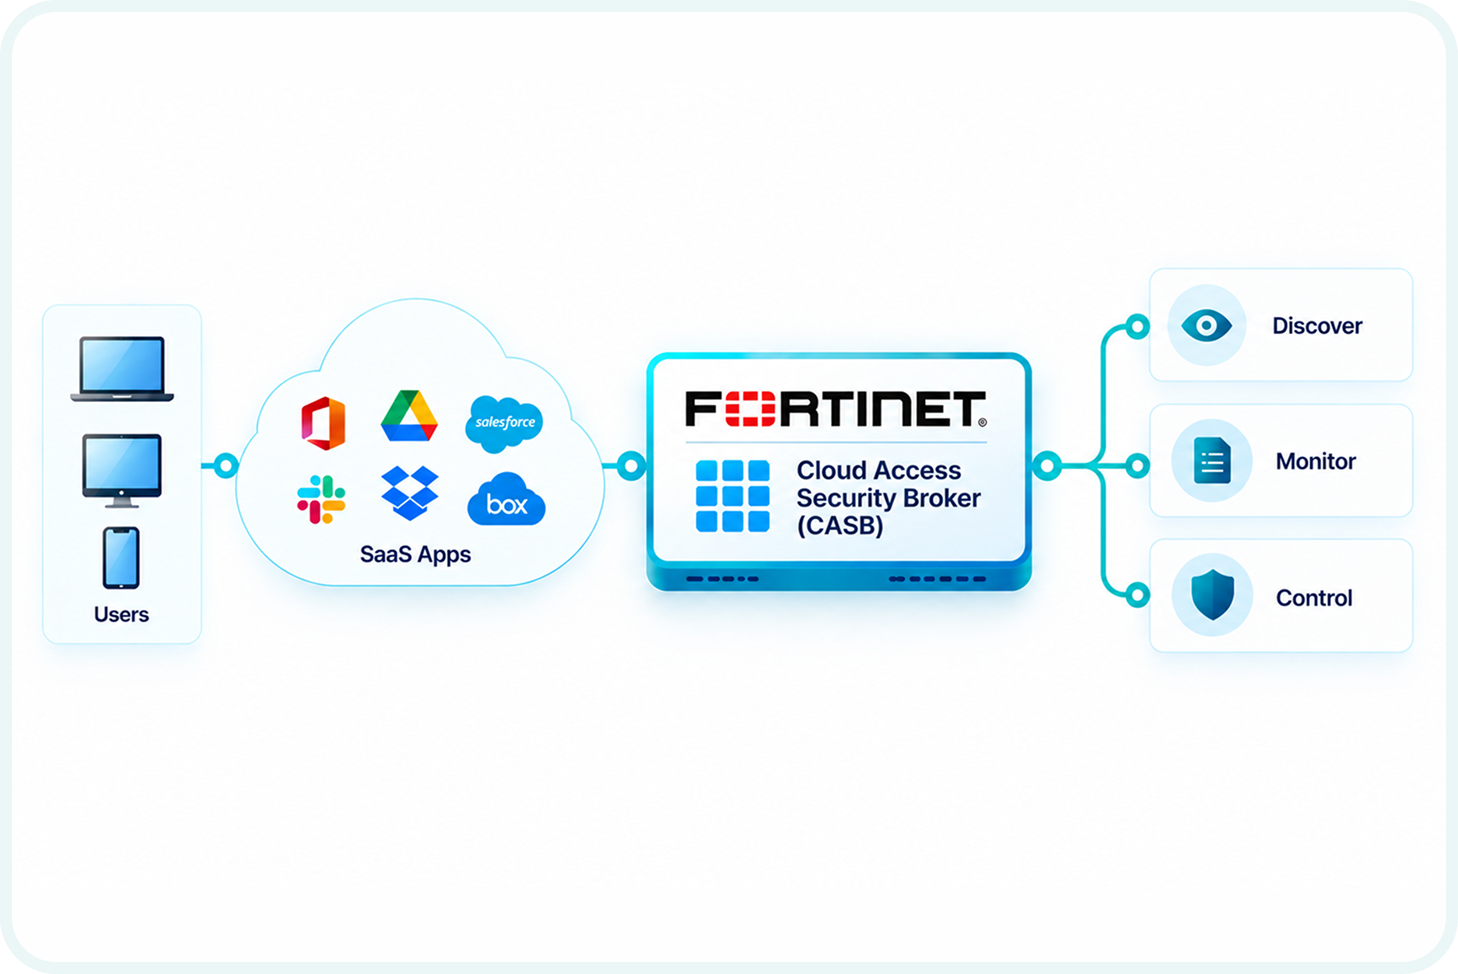
    Cloud Access Security Broker (CASB) 

    Visibility into every SaaS application in use, both sanctioned and unsanctioned. Shadow IT surfaces automatically. Data shared to personal cloud storage or unapproved platforms is visible and can be controlled. 
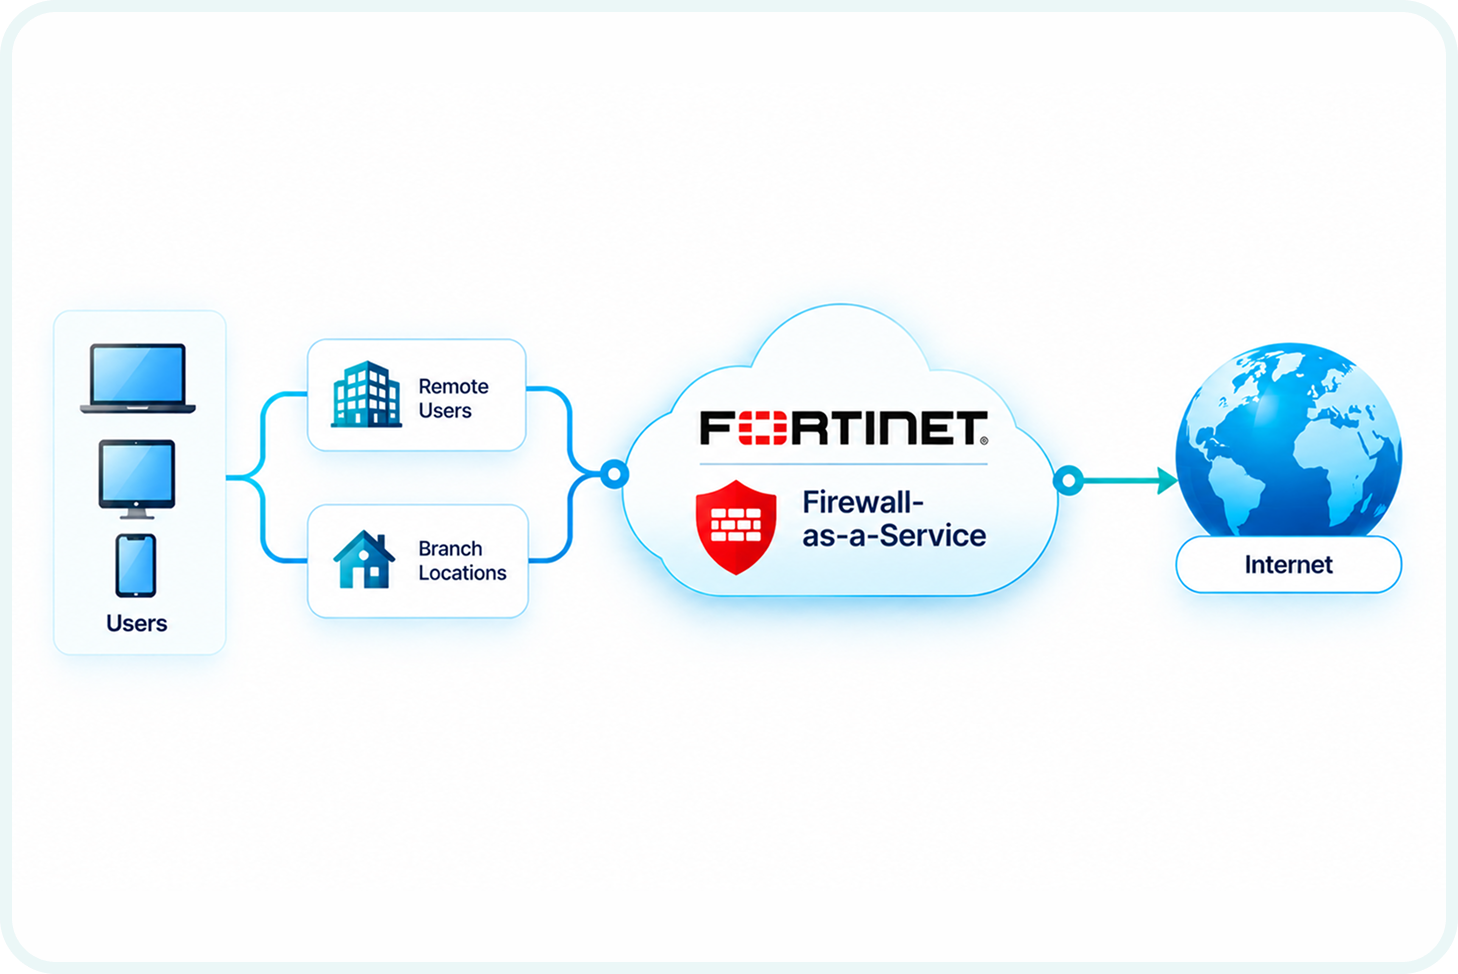
    Firewall-as-a-Service 

    Cloud-delivered firewall capability for users and locations without a physical FortiGate appliance, applying the same policy as the rest of the Fortinet estate. 
    Why Single-Vendor SASE Outperforms a Multi-Tool Stack

    Who Fortinet SASE Is the Right Fit For

    Multi-site businesses needing consistent policy

    When every site needs the same security policy and the management overhead of separate per-site appliances is growing, SASE centralises policy management while keeping enforcement close to each user and location. 

    Cloud-first and hybrid workforce businesses

    SaaS-dependent businesses where staff work from home, client sites or multiple office locations, and where VPN-based remote access is creating performance complaints or leaving security gaps for traffic that goes direct-to-internet. 

    Businesses already running Fortinet SD-WAN or FortiGate

    FortiSASE connects to existing deployments with no additional licence, making this an extension of an investment already made rather than a new procurement. Contact eComms to confirm compatibility with your current Fortinet configuration. 

    How eComms Manages Fortinet SASE

    eComms designs and manages Fortinet SASE end to end. The service covers architecture design based on your user count, site layout and cloud application profile, FortiSASE deployment and configuration, integration with any existing FortiGate or SD-WAN infrastructure, and ongoing management from our Melbourne NOC including policy updates, incident response and monthly reporting. Because eComms manages the SD-WAN, firewall and connectivity layers for many customers alongside SASE, the security architecture is integrated with the broader network from day one. For the full Fortinet capability range, see the Fortinet solutions hub. 

    FORTINET UNIFIED SASE (1)

    EDUCATION | FORTINET UNIFIED SASE | BRISBANE QLD | ~2,000 DEVICES

    Extending the same security policy to every student device, wherever it goes

    The Challenge:

    An independent Brisbane school with approximately 1,400 students and 2,000 managed devices needed consistent protection whether a device was on campus, at home, or anywhere in between.

    How the Product Solved It:

    Outcome:

    Why Businesses
    Choose eComms

    Answers to common questions about our managed phone systems, connectivity solutions, carrier network, and ongoing support services.

    What is SASE and how is it different from a VPN?

    SASE stands for Secure Access Service Edge. A VPN creates an encrypted tunnel from a remote device to the corporate network, giving access but applying minimal security policy during the session. SASE is a broader architecture that converges network connectivity and security into a single cloud-delivered platform. Every user, whether in the office or remote, is subject to the same security policy: web filtering, zero trust access control, threat inspection and application visibility. Fortinet Unified SASE delivers all of these from one platform. See the full Fortinet solutions hub for the broader Fortinet product range.

    Single-vendor SASE means every component, including SD-WAN, Secure Web Gateway, ZTNA, CASB and cloud firewall, comes from one vendor and runs on one operating system. The alternative is assembling these from multiple vendors and integrating them manually. Single-vendor SASE matters because consistent policy applies everywhere rather than only where each individual product is deployed, threat intelligence from one layer informs all others, and management uses one console. See Fortinet SD-WAN and Fortinet NAC for more on how the Fortinet stack integrates. 

    Universal ZTNA (Zero Trust Network Access) replaces broad VPN tunnels with precise per-application access. Before a user can reach an internal application, they authenticate and their device posture is checked. Fortinet's Universal ZTNA is included in the Fortinet SASE platform and is available at no additional licence cost for businesses already running FortiGate firewalls or Fortinet Secure SD-WAN, making it an extension of an existing deployment. 

    Yes. FortiSASE connects to existing FortiGate and SD-WAN deployments without an additional licence, extending consistent security policy to remote users without replatforming on-site infrastructure. Contact eComms to review how FortiSASE would fit with your current Fortinet configuration. 

    Fortinet SASE scales from small multi-site businesses to large enterprises. The architecture scales to the number of users and sites in the deployment. For a business with 50 staff across three locations and significant remote working, SASE addresses the same problem as for a 500-person enterprise: consistent security policy for every user regardless of where they connect from. eComms sizes the FortiSASE deployment based on your user count and site profile. Start with a conversation at contact us. 

    If your business is running a VPN, a separate web filter and per-site firewalls from different vendors, eComms can show you what consolidating those into Fortinet Unified SASE would look like for your environment, including the cost comparison across the contract term. The Melbourne team designs the architecture, manages the deployment, and runs the ongoing platform. See network security solutions for the broader security capability or contact eComms to start the conversation. 

    Consolidate Your Security Tools
    Under One Managed Platform

    Email our CX team: sales@ecomms.com.au